The modern cybersecurity landscape of 2026 has witnessed a sophisticated evolution in social engineering tactics where attackers no longer merely steal passwords but hijack active authenticated sessions directly. While traditional phishing attempts often involve fraudulent websites designed to harvest credentials, device code phishing exploits legitimate authentication protocols to bypass even the most robust multi-factor authentication systems. This specific method focuses on the OAuth 2.0 device authorization grant, a feature originally intended to simplify logins on devices with limited input capabilities, such as smart televisions, office printers, or specialized IoT hardware. By manipulating this convenience-oriented feature, cybercriminals can gain full access to an account’s tokens without ever knowing the user’s password, making it one of the most persistent and dangerous threats facing both individual users and large-scale organizations today. Understanding the mechanics of these session-based attacks is essential for maintaining digital security in an era where traditional defense perimeters are increasingly porous.
Building a resilient defense requires a deep dive into the technical exploitation of the Microsoft identity platform, which has been a primary target for actors like Storm-2372 and Midnight Blizzard throughout the current year. These groups have demonstrated that the strength of a password is irrelevant if a user can be persuaded to enter a short, eight-character code into a genuine Microsoft login page. Because the sign-in occurs on a legitimate domain, standard security advice—such as checking the URL for suspicious characters—fails to provide protection, as the page itself is completely authentic. The danger lies in the fact that the authentication session being authorized belongs to the attacker, not the victim, effectively turning the user’s own security protocols against them. As these campaigns have surged in mid-2026, the necessity for specialized recovery steps and advanced conditional access policies has become a top priority for IT security teams worldwide who must now manage the fallout of stolen refresh tokens that can persist for weeks.
1. Technical Foundations: The OAuth Device Flow
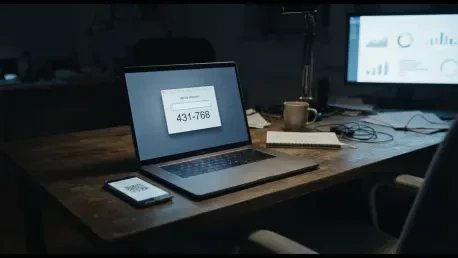
The OAuth 2.0 device authorization grant was developed to solve a specific usability problem: how to sign into an account on a device that lacks a keyboard or a modern web browser. In a standard, legitimate scenario, a user might open an app on a smart TV that displays a short alphanumeric code and a URL, such as a Microsoft device login page. The user then navigates to that URL on their smartphone or laptop, enters the code, and completes the authentication process. Because the user is already logged into their account on their phone, the television is granted an access token and a refresh token, allowing it to function without the user ever having to type a complex password on a remote control. This flow is a cornerstone of modern cross-device ecosystems, providing a seamless transition between secondary hardware and primary identity providers, but it assumes that the person requesting the code and the person entering it are the same individual.
Cybercriminals exploit this assumption by acting as the “input-constrained device” themselves, initiating a login request from their own infrastructure to generate a valid code. Once the attacker has this code, they must deliver it to a target and convince them to enter it on the official login portal within the code’s typical fifteen-minute lifespan. The brilliance of this attack lies in its simplicity: the attacker never needs to build a convincing fake website or bypass complex encryption. Instead, they rely on the victim to perform the heavy lifting of authentication, including providing the password and passing any secondary challenges such as biometric scans or hardware key prompts. Once the victim enters the code and approves the request, the attacker’s machine receives the resulting tokens. These tokens provide the same level of access as the victim, often including the ability to read emails, access cloud storage, and even move laterally within a corporate network to target other high-value accounts.
2. Strategic Exploitation: The Storm-2372 Campaign
Security researchers have closely monitored the activities of a cluster known as Storm-2372, which has been identified as a significant driver of device code phishing activity throughout early to mid-2026. This group, often associated with sophisticated state-aligned interests, has moved beyond generic spam to highly targeted social engineering campaigns aimed at government agencies, NGOs, and the technology sector. Their strategy often begins with establishing rapport through messaging platforms such as WhatsApp or Microsoft Teams, where they pose as recruiters, industry peers, or technical support personnel. By building a veneer of credibility over several days or weeks, the attackers create a psychological environment where the victim is less likely to question a request to “verify” their identity or “join” a high-profile virtual meeting using a provided code. This transition from social interaction to technical exploitation is the hallmark of modern session-based phishing.
The operational overlaps between Storm-2372 and established groups like Midnight Blizzard suggest a broader, more organized effort to gain initial access to sensitive environments. Once access is achieved through a stolen token, these actors have been observed using the Microsoft Graph API to programmatically search through mailboxes for sensitive keywords like “admin,” “credentials,” or “confidential.” This allows them to move quickly before a breach is detected, often exfiltrating data or setting up persistence by registering their own devices within the target organization’s directory. In many cases observed in 2026, the attackers have utilized regional proxies to ensure that their login activity matches the geographic location of the victim, thereby evading automated “impossible travel” alerts and other heuristic security checks. This level of operational security makes the detection of active device code phishing sessions exceptionally difficult for standard monitoring tools, requiring a shift toward more granular identity auditing.
3. Psychology of the Lure: Deceptive Tactics
The effectiveness of device code phishing relies almost entirely on the quality of the “lure,” or the story used to convince the victim to enter the code. Attackers have become adept at mirroring the professional language and branding of the tools people use every day, such as OneDrive, SharePoint, and Signal. A common tactic involves sending a legitimate-looking email invitation to a prestigious event or a mandatory corporate briefing. When the user clicks the link to join, they are presented with a message stating that for security purposes, they must enter a “meeting ID” on a Microsoft verification page. The “meeting ID” is, in reality, the device code generated by the attacker’s session. Because the instructions lead the user to a genuine Microsoft domain, the user feels a false sense of security, believing they are simply following a standard multi-factor authentication protocol required by their organization.
Moreover, the time-sensitive nature of these codes is used as a psychological weapon to induce panic and bypass critical thinking. Phishing messages often emphasize that the code will expire in mere minutes, creating a sense of urgency that discourages the victim from reaching out to their IT department for verification. Some lures have even evolved to simulate internal IT support calls, where a “help desk representative” guides the user through the process of entering the code over the phone under the guise of “fixing a synchronization error” or “applying a critical security patch.” In these scenarios, the human element becomes the weakest link, as the attacker leverages the trust inherent in professional relationships. By the time the victim realizes that the “meeting” or “patch” does not exist, the attacker has already secured a refresh token and potentially exported sensitive data from the user’s cloud environment.
4. Recovering Control: Initial Response Steps
If you only received the suspicious message and did not click any links, you can jump straight to Step 3. However, if you interacted with the link or entered any information on the page, you must complete every action listed below, beginning with your password. If you submitted a password after following a link from the phishing message, assume the attacker now has it. Navigate to the service provider’s official website by manually typing the address into your browser—do not use any links from the email. Create a unique password you haven’t used elsewhere and update it on any other accounts that shared the old one. If the provider offers an option to “sign out of all other sessions,” use it immediately. This action is critical because it invalidates the current session tokens that the attacker may be using to maintain access to your account, effectively cutting off their immediate line of sight into your data and preventing further unauthorized actions.
Following the password reset, the focus must shift to hardening the account against future attempts. Set up two-step verification so that any new login requires a code from your mobile device or an authenticator app. This ensures a stolen password alone isn’t enough to access your account. Activate this on your email first, then on banking, shopping, and social media accounts. While in your settings, verify that your recovery phone number, backup email, and email forwarding rules haven’t been altered by an intruder. Attackers frequently modify these settings to ensure they can regain access even after a password change, such as by setting up a silent forwarding rule that sends copies of all your incoming emails to an external address. Thoroughly auditing these settings is the only way to ensure that the attacker has not left behind a “backdoor” that would allow them to re-compromise the account at a later date.
5. Mitigation and Cleanup: Reporting and Scanning
Instead of just hitting delete, use the reporting tools in your mail client. In Outlook, select Report > Report phishing; in Gmail, use the three-dot menu to select Report phishing. This helps your provider block the scam for others. Do not engage with the sender or click any additional links. If this is a professional account, send the email to your workplace IT department as an attachment before removing it. Reporting is a vital community service in the 2026 threat landscape, as it feeds the global threat intelligence databases that allow security filters to recognize and block similar lures for millions of other users. By taking the time to report the message, you are effectively helping to dismantle the attacker’s infrastructure and reducing the overall success rate of their campaign.
Furthermore, if the phishing attempt involved downloading or opening a file, you must check your computer for malware. In Windows 10 or 11, go to Windows Security > Virus & threat protection > Scan options. Choose Microsoft Defender Antivirus (offline scan) and click Scan now. Your computer will reboot to perform a deep search, which usually takes about 15 minutes. Ensure your work is saved before starting. While device code phishing itself is an account-level attack, many campaigns are multi-staged and may attempt to drop a keylogger or a remote access trojan (RAT) onto your system to capture future credentials. An offline scan is particularly effective because it runs in a trusted environment before the operating system and any potential malware fully load, allowing the security software to identify and remove persistent threats that might otherwise hide from standard, real-time protection shields.
6. Professional Accountability: Coordinating With IT
If you have already submitted a code into a login box, you must act immediately. Since there is no single “undo” button, follow these actions in order. For workplace or school accounts, notify your administrators right away. Tell them exactly when you entered the code. This allows them to investigate the breach and cancel any active session tokens before the attacker can do more damage. Transparency is key in these situations; the faster the IT team knows about the incident, the more effectively they can isolate the affected account. Professional IT departments in 2026 have specific incident response playbooks for device code phishing, but these protocols rely on timely user reporting to be effective. Delaying the report by even an hour can give an attacker enough time to exfiltrate an entire mailbox or pivot to other sensitive internal systems.
Once the report is filed, ask your IT team to “revoke refresh tokens.” This is a specific administrative action (often done via Microsoft Graph) that forces the attacker out of your account. This step is vital because it terminates the attacker’s persistent access. In many cases, simply changing a password does not automatically invalidate the OAuth tokens that were issued during the phishing event. These tokens can remain valid for a significant period, allowing the attacker to continue accessing the account without needing to log in again. By specifically revoking these tokens, the administrator ensures that any current session associated with the attacker is immediately killed, requiring a fresh—and legitimate—authentication process for any further access. This administrative intervention is the only way to guarantee that the attacker’s foothold has been completely removed from the organizational cloud environment.
7. Forensic Investigation: Reviewing History and Devices
After the initial revocation, have your security team look for “risky sign-ins” or “newly registered devices.” Attackers often register their own hardware to your account to maintain a foothold. Any device you do not recognize should be removed instantly. This step is particularly important because a registered device may be granted a “Primary Refresh Token,” which can bypass certain multi-factor authentication requirements in the future. By auditing the list of connected hardware, the security team can identify exactly which devices belong to the user and which were surreptitiously added by the threat actor. This forensic look at the account’s history also helps in determining the scope of the breach, such as identifying if the attacker accessed specific sensitive documents or used the account to send further phishing lures to other employees.
Once the administrator has cleared the active sessions, change your password using a device you know is secure. You may be required to set up your multi-factor authentication methods again during this process. This serves as a “reset” for your digital identity, ensuring that all credentials and second-factor methods are fresh and uncompromised. It is also an opportune time to review the permissions granted to third-party applications. Attackers sometimes use their temporary access to grant broad permissions to a malicious app they control, which would allow them to maintain access even after password changes and session revocations. Cleaning up these application permissions is a critical but often overlooked part of the recovery process that ensures long-term security. Only after these forensic and restorative steps are complete can the account be considered truly secure and ready for normal use again.
8. Broadening the Scope: Personal Account Management
If you do not have an IT department (for a personal account), go to your account’s security dashboard. Manually change your password, check the “Recent Activity” log for locations you don’t recognize, and select the option to “Sign out of all devices.” This is also the best time to switch to a more secure login method, such as a passkey. For personal users, the responsibility of being your own “administrator” can be daunting, but most major providers have streamlined these security dashboards to be user-friendly. Reviewing your recent activity can provide peace of mind or early warning; if you see a successful login from a foreign country or an unfamiliar IP address at the exact time you entered the phishing code, you have definitive proof of a compromise. Addressing these issues immediately prevents the attacker from using your personal account to target your friends, family, or financial institutions.
Inform colleagues and friends that your account may have been compromised. Warn them to be skeptical of any messages or file links sent from your address around the time the incident occurred, as the attacker may have used your account to spread more phishing links. This is especially important for personal accounts, as your contacts are likely to trust a message coming from your real email address. A quick warning can prevent a “chain reaction” of infections within your social circle. Furthermore, while this specific type of phishing targets your account rather than your software, a system scan is still a wise precaution. If the initial message prompted you to download anything, a full scan will ensure no secondary malware was left behind. Protecting your personal digital footprint in 2026 requires a proactive approach that combines technical tools with clear communication to mitigate the social damage an attacker can cause.
9. Organizational Policy: Blocking the Flow
Microsoft recommends getting as close as possible to a unilateral block on the device code flow, and allowing it only in well-documented, secured uses such as legacy tooling that cannot be updated. For most organizations, the device code flow is a luxury rather than a necessity, and the risk it poses far outweighs the convenience it provides. Administrators should begin by auditing the current use of this flow within their environment to identify any legitimate business processes that might be disrupted by a block. In many cases, IT teams find that the flow is rarely used by standard employees, making a broad restriction a highly effective and low-impact security measure. By moving toward a “block by default” stance, organizations can effectively eliminate this entire category of phishing attacks, forcing attackers to find more difficult and less reliable methods of entry.
To implement this, administrators can create a Conditional Access policy within the Microsoft Entra admin center that specifically targets the “Authentication Flows” condition. By selecting the “Device code flow” and setting the access control to “Block,” the organization can prevent any unauthorized initiation of this sign-in method. It is advisable to exclude emergency “break-glass” accounts from this policy to ensure that administrators can still access the system in extreme scenarios. Starting the policy in “Report-only” mode allows the IT team to monitor for any unintended consequences before fully enforcing the block. This strategic shift from reactive cleanup to proactive prevention is the most effective way to handle the surge of session-based attacks seen throughout 2026, as it removes the underlying mechanism that the attackers rely upon to bypass traditional security perimeters.
10. Future Considerations: Phishing-Resistant Identity
Building a sustainable defense against modern phishing requires a shift toward phishing-resistant authentication methods that do not rely on shareable codes or easily intercepted tokens. Technologies such as FIDO2 security keys and platform-based passkeys offer a superior level of protection because they bind the authentication process to a specific physical device and a specific web domain. Unlike a device code, a passkey cannot be “phished” in a traditional sense; the cryptographic handshake between the user’s device and the service provider will simply fail if the domain does not match exactly. As we move through the latter half of 2026, the adoption of these passwordless standards is becoming the new baseline for secure organizations, providing a robust answer to the vulnerabilities inherent in legacy authentication flows and the social engineering tactics that exploit them.
In conclusion, the rise of device code phishing served as a critical wake-up call for the cybersecurity community, highlighting that even the most trusted platforms can be turned into vectors for attack. Users and organizations that took decisive action by revoking tokens, auditing registered devices, and implementing conditional access policies successfully mitigated the risks associated with these sophisticated campaigns. The lessons learned during the peak of this activity led to a broader movement toward identity-centric security, where the focus shifted from protecting the perimeter to securing the individual session. By adopting a culture of skepticism toward unsolicited requests and embracing hardware-based security, the digital community moved toward a more resilient future where the convenience of cross-device connectivity no longer came at the expense of fundamental account security. Actionable steps taken in the wake of these threats ultimately strengthened the global posture against session hijacking and improved institutional response times across all sectors.