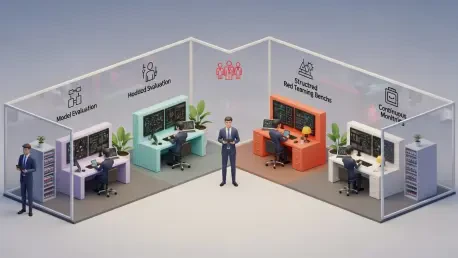
Breaches of trust no longer hinge on classic bugs alone but on opaque, fast-moving AI behaviors that can misread context, misapply tools, and mislead users at scale before anyone notices. Enterprises, particularly banks, now face a quality mandate that spans model behavior, safety, and governance,
Speed alone rarely wins the race when building mobile apps in Qatar, because success hinges on fluency with the country’s language norms, regulatory rails, and public-sector integrations that quietly determine whether a product ships on time, earns trust, and scales without rework. That reality has
Sebastian Raiffen sits down with Anand Naidu, a full‑stack development expert who’s spent years balancing delivery speed with the realities of software supply chain risk. Anand has led teams through dependency sprawl, CI/CD hardening, and SBOM-driven governance, translating security principles into
Ransomware crews now pivot across cloud accounts in minutes, phishing emails read like a colleague wrote them, and deepfake voices authorize wire transfers with eerie confidence, forcing security teams to choose between slow caution and fast mistakes. Against that backdrop, AI-enabled cybersecurity
Introduction to AI-Driven Testing in Fintech Payment rails rarely pause, risk models never sleep, and yet software changes ship constantly, so quality now depends on systems that learn where money, policy, and code will collide before customers ever feel the jolt. The shift under review is not
Context and Stakes Credentials multiplied faster than services could be secured, and pipelines turned into high-speed conduits for risk unless secrets were handled with rigor from commit to production. That pressure reshaped how teams think about identity, trust, and automation. In cloud-native